1、问题说明
Cookie 未配置 SameSite 属性或配置不合理,可能会导致跨站请求伪造(CSRF)
SameSite 属性配置不合理情况如下:
1)samesite=None;但无Secure;
2)samesite=Secure;但无其他配置信息
2、操作说明
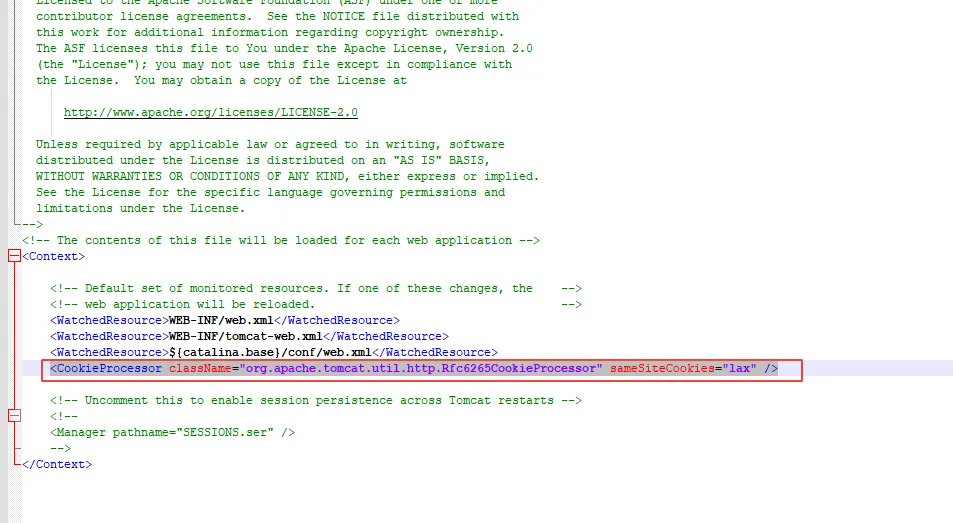
打开 CMSServerV6\tomcat\conf\context.xml 文件,在 <Context> 标签内添加 CookieProcessor 配置。重启web服务。
<CookieProcessor className="org.apache.tomcat.util.http.Rfc6265CookieProcessor" sameSiteCookies="lax" />