1 problem description
Cookies are not configured with SameSite attributes or are not configured properly, which may lead to Cross- Site Request Forgery (CSRF)
The unreasonable configuration of SameSite attributes is as follows:
1)samesite = None; but no Secure;
2)samesite = Secure; but no other configuration information
2 operating instructions
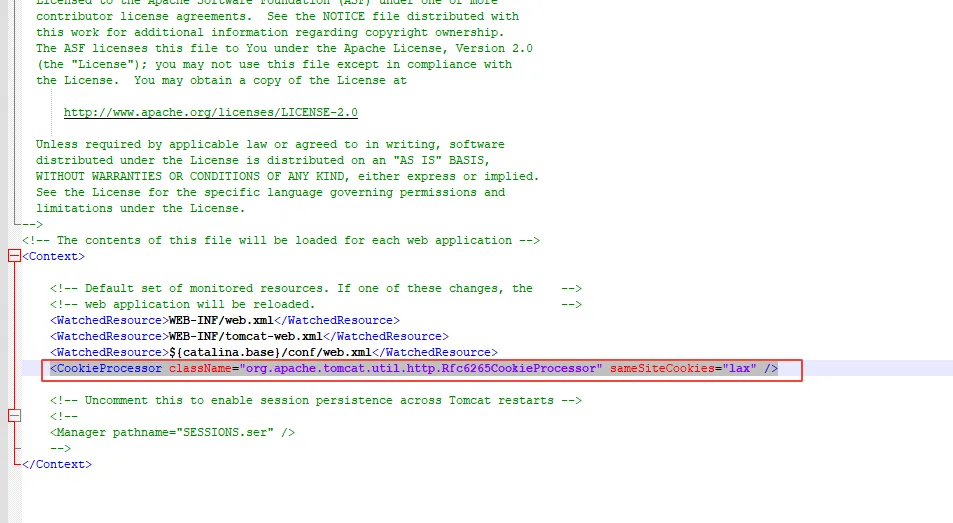
Open the CMSServerV6\tomcat\conf\context.xml file and add the CookieProcessor configuration in the <Context> tab. Restart the web service.
<CookieProcessor className="org.apache.tomcat.util.http.Rfc6265CookieProcessor" sameSiteCookies="lax" />